New Gartner® research — ToothPic is named a Sample Vendor in the Emerging Tech Impact Radar: Disinformation Security, September 2026.

Read more

Fraud prevention · Hardware-anchored device signal · Made in EU

Big fraud losses share one thing: a device that was never identified.

Mules. Deepfakes. Takeover. Approval fraud.
Every one runs on a real phone. ToothPic tells you which phone — from the camera sensor your customer already carries.

FIDO2 · U2F certified Gartner front runner ’26
+741%
iOS camera-injection attacks on onboardingGlobal · 2025
€95M
wired out on one AI voice-clone callFideuram, Italy · 2026
524K
mule accounts flagged in one monthIndia · 2025
1M+
victims of a single phishing kitSmishing Triad · 120+ countries

Why it keeps happening

Your controls score probability — never possession.

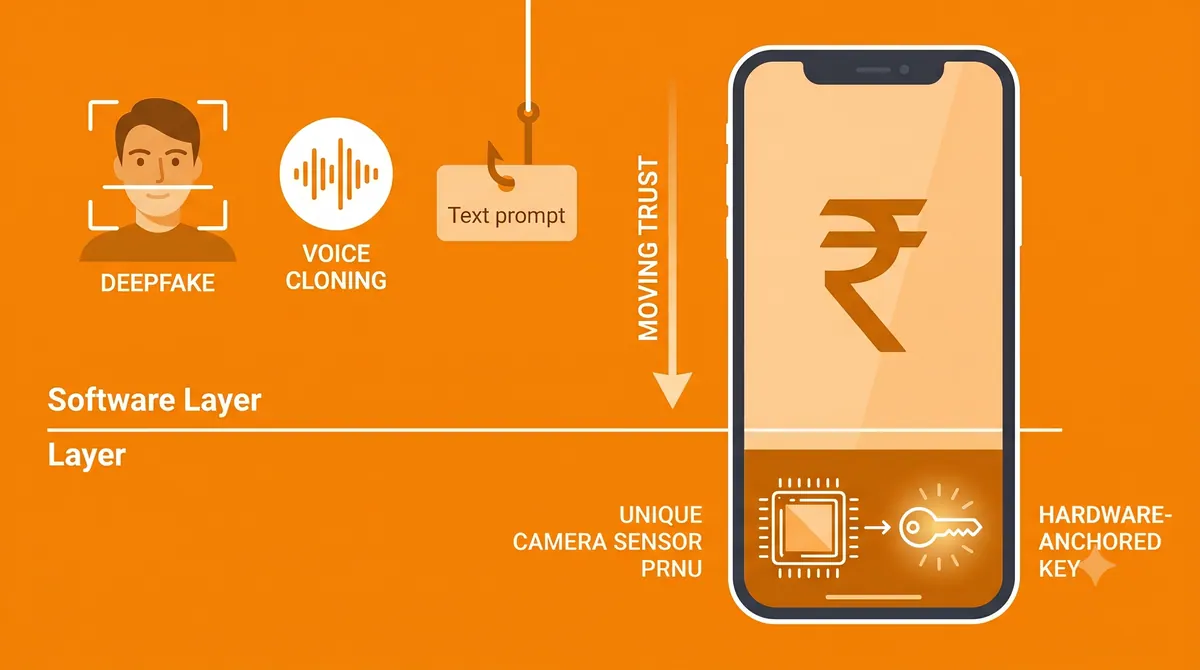
Device intelligence, behavioural models, OTPs, liveness and synced passkeys are all software signals — and generative AI manufactures software at zero marginal cost. A probability score can always be argued with.

Mules, deepfakes and takeover look like different crimes. They share one blind spot: nothing proves which physical handset is in play.

Anything known can be phished
Anything shown can be faked
Any person can be synthesised
Any camera feed can be injected

The physics

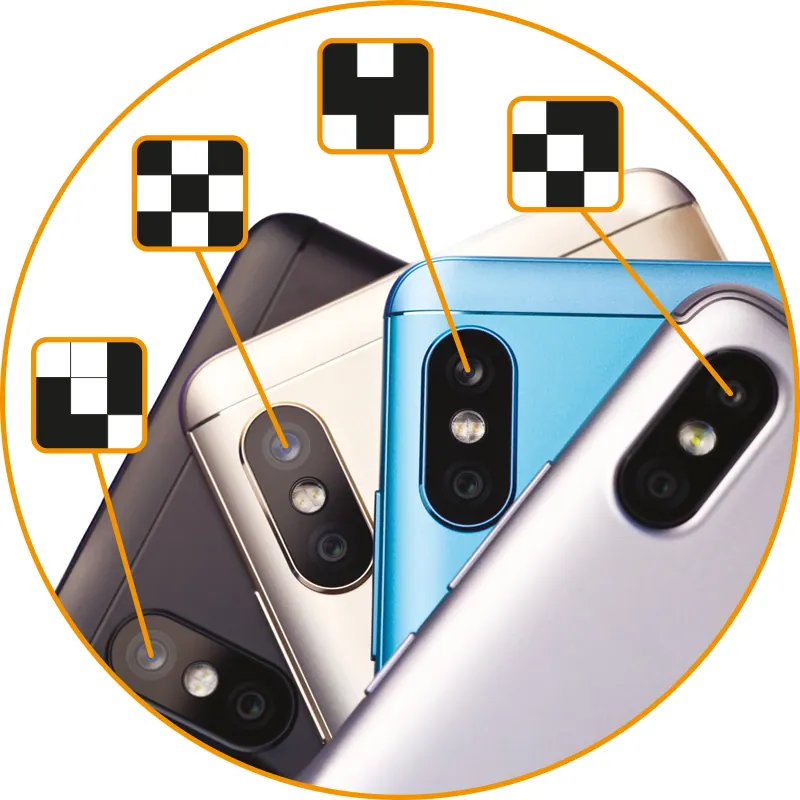
The identifier is the camera sensor.

During manufacturing every sensor develops microscopic, unclonable imperfections — Photo-Response Non-Uniformity (PRNU), a physical unclonable function. ToothPic turns it into a standard key, only for the instant it is needed.

1

Read

Factory-random silicon noise (PRNU) is read through the standard camera permission. No photo is taken or stored.

2

Rebuild

A standard elliptic-curve private key is regenerated in ~30 ms to sign the challenge.

3

Vanish

The key is destroyed immediately after signing. Nothing on the phone, nothing in a database.

0 secrets at restDefeats injection attacksISO 30107-3 · CEN/TS 18099

The fraud landscape

Which of these is costing you?

Six different crimes, one blind spot. If any of these sits on your board report, ToothPic answers all six with a single signal — for banks, payment providers, insurers and fintechs.

Mules & synthetic identities

The fraud

Clean accounts are rented or manufactured at scale to move stolen money.

What ToothPic does

One handset operating many accounts becomes visible — a mule ring shows up as a pattern, not a hunch.

The scale of it

524,000+mule accounts flagged in India in a single month
Onboarding & camera injection

The fraud

Face-swapped IDs and injected video are pushed straight into KYC. Liveness checks cover presentation attacks only.

What ToothPic does

Injected frames carry no sensor noise, so they cannot sign. The attack fails below the camera.

The scale of it

+741%iOS camera-injection attacks on onboarding, 2025

Account takeover & OTP bypass

The fraud

SIM swaps, OTP bots and real-time phishing kits defeat 2FA and take the account.

What ToothPic does

The handset cannot be ported, relayed or phished — only the real phone can answer.

The scale of it

96,000+victims of the Tycoon 2FA kit before takedown

Deepfake-authorised transfers

The fraud

Cloned voice and video are used to authorise a payment that nobody questions.

What ToothPic does

A push challenge the real handset must sign. Synthetic media has no sensor, so it is disqualified.

The scale of it

€95Mwired out of Fideuram after an AI voice-clone call

Wallet & NFC provisioning

The fraud

Phished cards are loaded into wallets on phones the fraudster controls.

What ToothPic does

Provisioning is bound to a device that can be named, so a stranger’s phone is refused.

The scale of it

1M+victims of the Smishing Triad kit across 120+ countries

Helpdesk & approval fraud

The fraud

Service desks are socially engineered, and signing payloads are manipulated in transit.

What ToothPic does

The desk stops guessing and asks the device to sign for itself.

The scale of it

€516Madviser-manipulation fraud in France, 2025 (+34%)

The evaluation

The only signal that is deterministic.

Every other row produces a score you must tune. This one produces an answer.

Integration

Beside your fraud stack — not instead of it.

One SDK in the app you already ship. No new platform, no database changes.

Proof

Validated. Certified. In production.

Gartner front runner

Emerging Tech: Startups to Watch for Deepfake Detection, April 2026 — top category of 42 startups analysed.

4 patent families

US · EU · IT · CN · JP · IL · KR, 20-year terms.

FIDO2 + U2F certified

Standards-compliant: no proprietary protocol to adopt. Politecnico di Torino spin-off, two EU Seals of Excellence.

4 paid EU deployments

Insurance, payments and academia — live in production.

400M+ user proof of concept

Validated on a real-time payments platform — proven at population scale, not pilot scale.

Gartner Sample Vendor

Emerging Tech Impact Radar: Disinformation Security, September 2026 — Trust and Authenticity for Physical AI.

In production

Some of our customers

A selection of the organisations running ToothPic in insurance, payments, public services and research.

  • Poste Italiane
  • Intesa Sanpaolo Assicurazioni
  • Value+
  • CSI Piemonte
  • Politecnico di Torino

Prove it

Don’t take our word for it. Take 90 days.

One flow, your own fraud baseline. Existing controls stay live throughout, and reversing costs one sprint.

Weeks 1–2

Scope

Together we pick one customer journey, agree what counts as success, and write down today’s numbers to measure against.

Weeks 3–10

Listen

The SDK runs beside your controls behind your feature flag. The signal is logged, not acted on. No customer can be declined by it.

Weeks 11–13

Decide

Devices behind many accounts, step-ups you never needed, good customers you turned away, devices that returned after a reset.

See how the pilot is de-risked

Ready to see it on your own fraud?

One flow, your own baseline, existing controls stay live — and reversing costs one sprint.